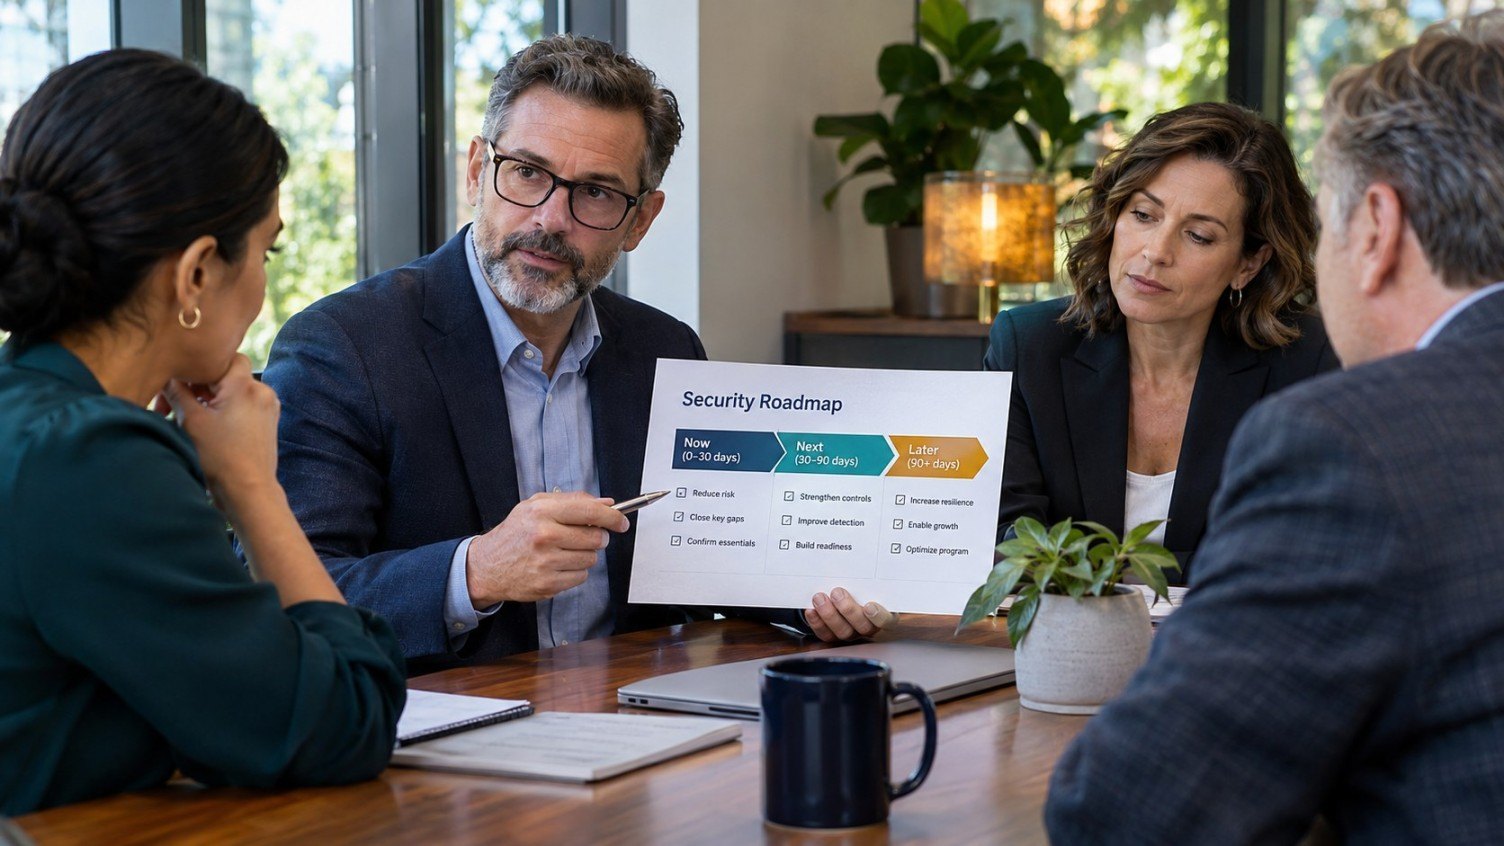
Sales needs security answers for a prospective customer. Engineering is planning a cloud migration. A director wants to know whether the business could recover from a serious incident. A virtual CISO helps leadership decide which problems need attention first and who owns the work.
What fractional security leadership looks like
A vCISO gives a company access to senior security leadership on an agreed basis. The role can shape strategy, translate risk for the board and coordinate priorities across teams. It needs a named executive sponsor and clear decision rights. Tool administration and day-to-day monitoring should have their own owners, whether those are internal teams or managed providers.
How CyberSeal adapts to the organisation
CyberSeal’s vCISO service combines security strategy, risk management, board advisory and strategic incident response. Depending on scope, the work can include a longer-term security roadmap, policy ownership, supplier risk, audit priorities and leadership reporting. The starting plan should reflect the company’s growth stage, customer commitments, delivery capacity and risk tolerance.
Explore CyberSeal’s vCISO Services.
If leadership needs a stronger baseline before committing budget, explore CyberSeal Security Assessments & Risk Management. If the gap is keeping the risk register, control evidence, and reviews current between leadership meetings, see CyberSeal GRC Services.
From discovery to delivery
- 1 Days 1–30Agree decision rights, meet business owners, and establish a risk baseline.
- 2 Days 31–60Turn priorities into a roadmap with owners, funding needs, and dependencies.
- 3 Days 61–90Run a leadership review, record decisions, and set the reporting cadence.
What CyberSeal vCISO onboarding looks like
Agree the mandate. Bring your business plan, customer security commitments, prior assessments, current risk register, and major technology changes. Include the executive sponsor, IT or engineering lead, and the people who control budget or accept risk. Agree which decisions the vCISO will advise on and who approves funding, policy changes, or exceptions.
Build a baseline with your team. Review evidence alongside interviews. Check whether incident contacts are current, who owns supplier reviews, and which business processes depend on untested recovery plans. Record which findings are confirmed and which need further investigation.
Set a roadmap that fits your capacity. CyberSeal’s service describes a 12–24 month security roadmap. Use the first 90 days to agree which outcomes come first, who implements them, and what funding or dependencies could affect delivery. A company facing an enterprise contract deadline may need to sequence the work differently from one preparing for a cloud migration.
Set the leadership rhythm. Agree how often to review the roadmap and report to executives, and when to escalate urgent issues. Decide who leads technical incident response, who coordinates executive communications, and who has approval authority during a crisis. Use the first leadership review to test whether the briefing gives people enough information to make a decision.
What to check: The 90-day sequence is an example. Agree the actual milestones, meeting cadence and availability when you scope the engagement.
Practical details and examples
Start by defining the mandate with leadership
Decide what the virtual CISO is being asked to improve. A founder might want to answer larger customer security reviews. A finance leader may want a better basis for next year’s budget. A board might need a clear view of the organisation’s ability to recover from an incident. Name an executive sponsor and agree which decisions the vCISO can make, which ones require leadership approval, and how the vCISO will work with existing IT and security teams.
CyberSeal’s vCISO service covers strategy, risk management, governance, compliance oversight, executive reporting and a security maturity roadmap. Translate those responsibilities into outputs the organisation will use. A growth-stage SaaS business may need a roadmap aligned to customer contracts and upcoming platform releases. An established enterprise may want an independent view of risks across business units. The same leadership experience can serve both, but the meeting cadence, evidence and decisions will differ. Agree those differences before the work begins.
Days 1–30: Learn how the organisation actually runs
Meet with the sponsor, product leaders, IT, operations and the owners of customer obligations. Review the current roadmap, known incidents, architecture summaries and upcoming changes. Ask which business activities would be most affected by loss of access or availability. Record where the information is incomplete and who can verify it. During this period, avoid producing a long list of projects before the team understands what is feasible and which constraints cannot move.
Give leadership a short first readout: the few areas that deserve attention, what is already working and which facts are still missing. An example might be a company preparing to sign a large customer while onboarding a new cloud service. The first discussion could cover assurance commitments, recovery evidence and who approves new privileged access. The vCISO can explain why those issues matter while leaving the technical team enough space to choose the implementation that fits the platform.
Days 31–60: Turn competing needs into a roadmap
For each priority, write the business outcome, accountable owner, dependency and evidence of completion. If a project needs budget or capacity, be explicit about the trade-off. Improving access reviews might depend on identifying owners for several systems first. A recovery exercise might reveal that backing up data is only part of restoring the application. The plan should make these dependencies visible, so leadership can fund useful work rather than reacting to whichever report is longest.
Agree how the vCISO will support implementation. CyberSeal’s leadership offering is different from operating every tool. The vCISO may coordinate a decision, define the intended control and review progress while internal engineers or an agreed managed service make the change. Document who approves scope and risk. Set a practical rhythm for reviewing blockers, and use the same record to note why a decision was made and what would cause the company to revisit it.
Days 61–90: Show the board what has changed
Prepare a concise update that separates activity from outcomes. Rather than saying that a programme ran six workshops, explain the decisions that were made, what risks changed and which issues require executive action. If recovery remains uncertain, state what has been tested and where the evidence stops. Include upcoming commitments and the owner responsible for them. A report is useful when a board member can understand the decision needed without reading the entire technical backlog.
Agree the next operating cadence with the customer. Some teams will want ongoing strategic reviews, support for customer or audit discussions, and a clear escalation route when an incident affects business decisions. Others may only need a defined advisory project followed by an internal handover. Confirm what is included before promising availability. The first 90 days should leave the customer with a usable roadmap, named owners and a way to adjust priorities as the company grows.
What to ask when comparing vCISO proposals
Ask who will lead the work, how often they will meet your team, what they will deliver in the first three months and what their role is during an incident. Request a sanitised example of an executive risk report or roadmap. The best discussion starts with your business constraints and ends with a clear agreement about which decisions and deliverables the service will own.
Copyable one-page cybersecurity board briefing
Use one row per material risk or decision. Lead with what needs approval and when.
- Decision requested: Approve a recovery exercise for the billing platform before migration.
- Business impact: A prolonged billing outage could delay invoicing and affect collections.
- Evidence and uncertainty: Backups are configured. A timed restore for the full billing workflow is still pending.
- Recommendation and owner: The platform lead runs a controlled restore and confirms the business workflow with Finance.
- Deadline and verification: Complete the exercise before migration sign-off. Record actual recovery time and compare it with the agreed objective.
- Follow-up: If recovery misses the objective, bring the mitigation options and migration impact back to the sponsor.
Frequently asked questions
Can the vCISO work alongside our IT lead?
Yes. Agree who owns strategy and governance, who implements changes, and where decisions are shared.
What should the board get?
A short view of material risks, treatment progress and decisions that need approval, in business language.