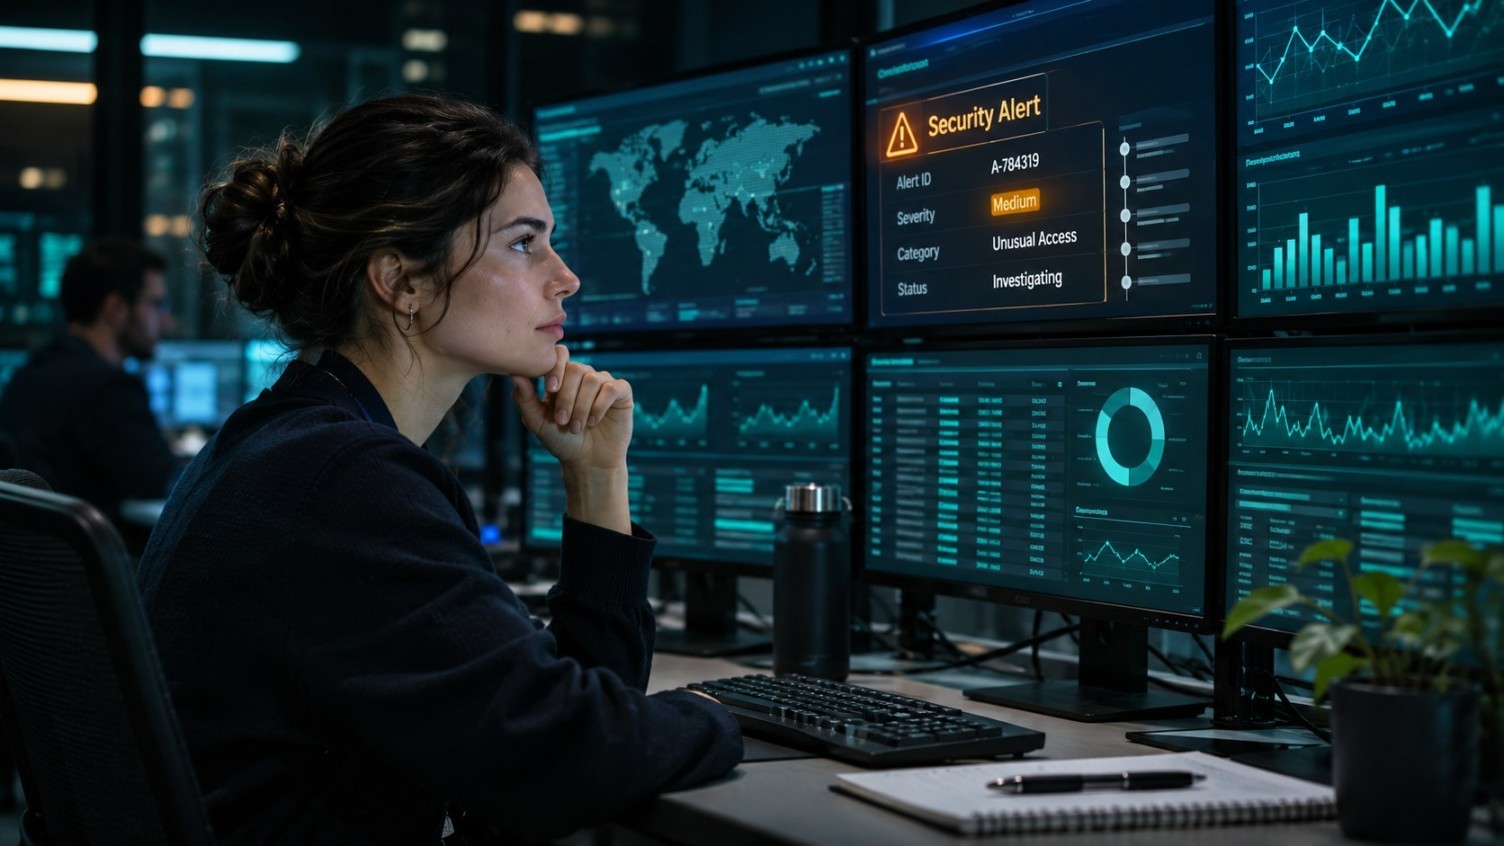
An employee account signs in from an unfamiliar location shortly after midnight. The endpoint tool reports unusual activity on the same laptop. Separately, neither alert tells the whole story. Together, they warrant investigation. When you evaluate a managed SOC, ask how the provider connects signals like these and what you will hear from them if the alert turns into an incident.
What a managed SOC should deliver
A security operations centre monitors agreed parts of your environment, investigates suspicious activity and escalates confirmed or credible incidents. Coverage is only as useful as the data feeding it. Ask which endpoints, cloud accounts, network devices and identities are covered, and how you will learn when a source stops reporting. Agree who can contain an incident and what requires your approval.
How CyberSeal gets your SOC running
CyberSeal’s 24/7 Managed SOC service covers monitoring, correlation, endpoint detection and response management, triage, threat hunting and guided response. Its tiered model separates first-line alert validation, deeper incident investigation and platform engineering. The starting point is your environment: the team can work with existing tools where the agreed scope allows, and tailor alerts to the assets and business processes that matter most.
From discovery to delivery
- STEP 01
Map the coverage
Agree the assets, telemetry, business hours, contacts and response boundaries. Identify anything critical that the SOC cannot yet see.
- STEP 02
Connect and validate
Bring in the agreed log sources. Confirm the signals arrive and that an analyst can trace them to the right device or account.
- STEP 03
Rehearse the handoff
Use a safe test alert to walk through triage, customer notification, decision authority and containment.
- STEP 04
Operate and tune
Review incident outcomes with your team, retire noisy detections and adjust coverage as systems or priorities change.
What to check: Ask for a sample escalation. It should tell you what happened, which assets are affected, what the SOC has already done, and what decision it needs from you.
Practical details and examples
Agree what an alert means to your business
Give the solution architect two or three incidents your organisation would care about: an employee account sending suspicious mail, an administrator accessing a sensitive cloud account from an unexpected device, or ransomware indicators on a file server. For each one, name the system owner, explain the business impact, and describe when you want the SOC to call. The exercise makes it easier to distinguish a serious incident from an alert that can wait for a morning review.
Build a coverage sheet around those scenarios. For identity, document which sign-in sources and administrator accounts are visible. For endpoints, confirm which operating systems and business units report. For cloud and network activity, record where the data comes from and which sources are out of scope. CyberSeal’s service includes threat intelligence and reporting alongside monitoring and investigation. Intelligence should help analysts interpret what they see in your environment; ask how they would explain the evidence behind a threat match to your team.
Walk through a plausible escalation before go-live
Consider a hypothetical customer with an international workforce. An employee signs in from a new location during an approved trip. By itself, the change is not necessarily suspicious. An endpoint alert and a new mailbox forwarding rule around the same time give the analyst more reasons to investigate. The case should distinguish what the tools recorded, what the analyst thinks happened, and what still needs checking. The employee’s travel plans are useful context; they do not automatically explain the other signals.
Before production monitoring starts, agree what the SOC is authorised to do in a case like this. It might gather evidence and notify an on-call owner, recommend revoking a session, or take an approved containment action if the integration and contract allow it. Your team needs a route to undo an action if it interrupts business. An exercise should also include an unreachable primary contact. Try the secondary number and check that it reaches someone with authority to make the decision, rather than another shared inbox.
Give the customer a role at every handoff
CyberSeal’s onboarding model can begin with an RFP, followed by an agreed contract and service levels, assignment of a solution architect, a customer-approved implementation plan, and a transition to ongoing operations. For a SOC, translate that sequence into decisions your team can review. Before signing the contract, compare which log sources and hours are covered, what constitutes a major incident, and what timelines apply to acknowledgement and notification. Clarify whether containment or forensics are included, available separately, or handled by your team.
During implementation, ask to see the test cases and sign off on the coverage and escalation workflow. At handover, keep a short guide with contact paths, incident roles, permitted actions and unresolved dependencies. The guide should name someone on the customer side who can raise changes: a new cloud account, an acquisition, a replacement endpoint product, or a different after-hours contact. Confirm who updates the monitoring scope and how you will know the change was picked up. This is particularly important when internal owners rotate but the service remains in place.
Use the service review to improve coverage
At the first review, separate activity from outcomes. A chart showing the number of alerts tells you the analyst workload. A short walkthrough of a real or rehearsed case tells you whether your team got enough information in time to make a decision. Ask for examples of detections that were added, sources that went silent and alerts that were tuned because they did not lead to action. Where metrics such as detection or response time are reported, agree what starts and stops the clock so the numbers are comparable.
Keep a shared list of changes with an owner and due date. For example, if a branch’s endpoint logs are not arriving, name the person responsible for the connection and set a test to verify restoration. If the SOC escalates an incident your team considers routine, agree what signal should make the next occurrence urgent. A useful review ends with clear decisions: what CyberSeal will change, what your team must provide, and which risk you are knowingly carrying until the work is done.
What to bring to the first conversation
Share an inventory at the level you are comfortable disclosing, the security tools you already operate, two incident examples with sensitive details removed, and your current escalation process. If you have an existing SOC, bring the problem you want to solve, such as missed after-hours alerts or an incomplete cloud view. Ask the proposed team to explain how it would onboard one critical system, demonstrate a detection and notify you. That example gives both sides a practical basis for discussing scope and cost.
Frequently asked questions
Do we need a new set of security tools?
Not necessarily. Start with the supported tools and licences you already have, then agree what needs to be added for the coverage you want.
Can the SOC isolate a device automatically?
That depends on tool support and the response authority you approve. Document it before the first real incident.