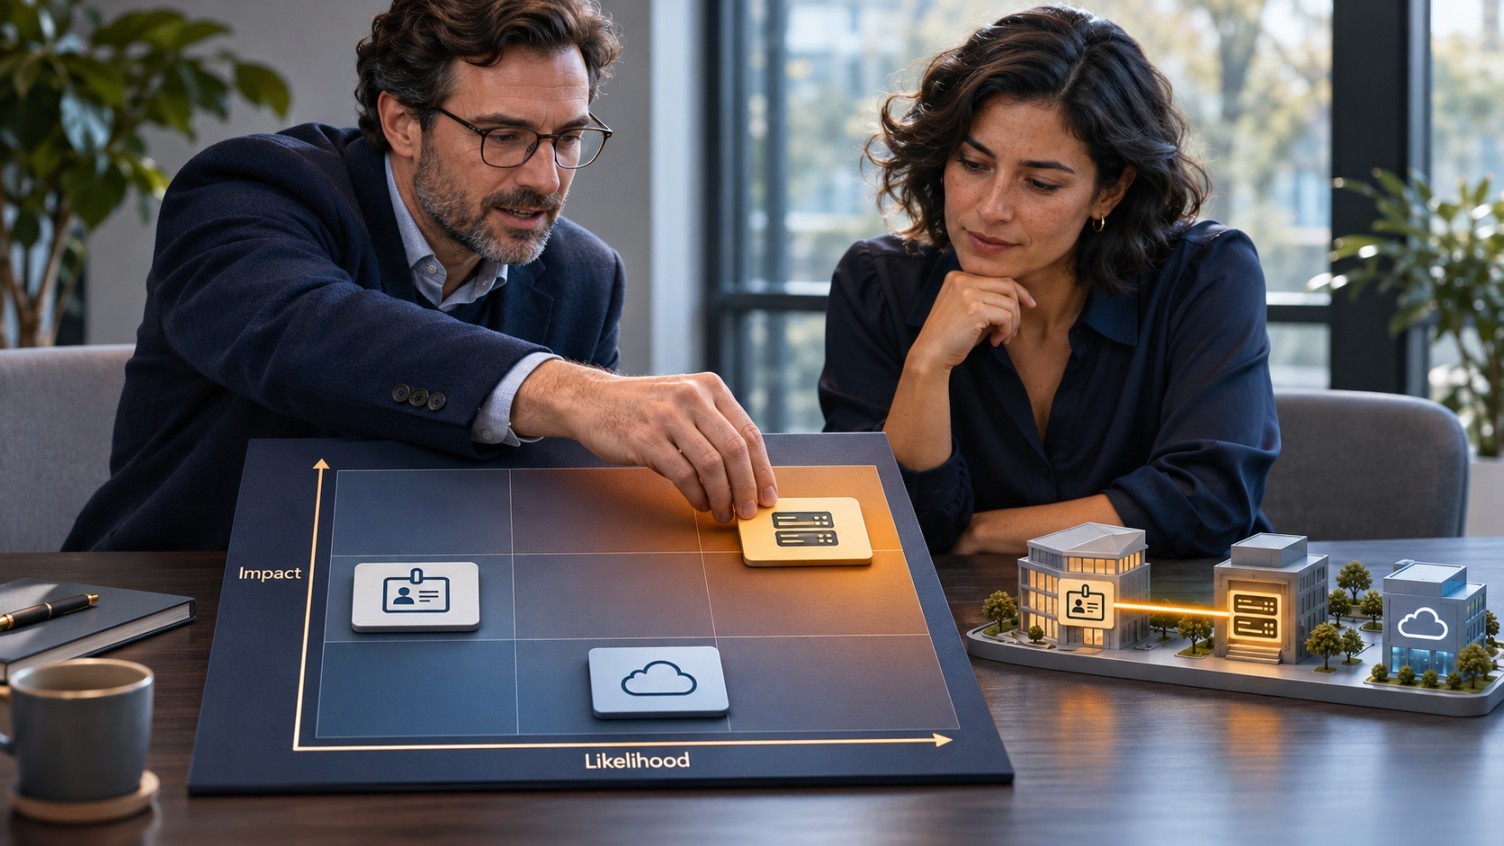
Three teams want budget for security work: one to redesign access, one to fix a cloud exposure and one to review a supplier. A useful assessment helps leadership decide what cannot wait, what can be treated temporarily and what requires more evidence.
Describe risks in terms a decision-maker can use
For each risk, write what could happen, which business process would be affected, how likely it is and what limits it today. For example, a vendor with standing administrative access presents a different risk if it can reach production backups than if it is confined to a test account. NIST’s risk assessment guide provides a structured method; the assumptions and scoring still need to match your environment.
For cloud applications, a simple data-flow diagram helps teams see where identities, services, and data cross trust boundaries. Microsoft’s Azure Well-Architected threat modelling guide shows how to structure that conversation. For hands-on configuration and architecture work, explore CyberSeal Cloud Security Services.
How CyberSeal tailors the assessment
CyberSeal identifies, classifies, prioritises, treats and tracks risks across the agreed scope. Its assessment work can cover information security governance, cloud and SaaS, applications, vendors, compliance mapping and identity. The team explains the impact in business language and works with owners on a practical treatment plan. Leadership can then see which actions need budget, authority or an explicit risk decision.
Explore CyberSeal’s Security Assessments & Risk Management.
If you need to maintain the register across departments, schedule treatment reviews, and track control ownership, see CyberSeal Governance, Risk & Compliance Services.
From discovery to delivery
- 1 IdentifyMap critical processes, assets, suppliers, and credible risk scenarios.
- 2 ClassifyRate likelihood and business impact using agreed criteria and evidence.
- 3 PrioritiseDecide which risks need immediate action, further evidence, or a planned fix.
- 4 TreatAgree a response, owner, due date, and evidence of completion.
- 5 TrackVerify the treatment and reassess the remaining risk.
What CyberSeal assessment onboarding looks like
Kickoff. Bring a list of critical services and suppliers, relevant architecture diagrams, recent findings, and upcoming decisions. Invite the business sponsor, security lead, and the owners who can explain how the services operate. Agree on the decision the assessment should support, such as which fixes to fund before a migration.
Evidence and scope. Agree which business units, systems, and suppliers are in scope, who can provide approved evidence, and how it will be shared. Review relevant identity settings, configurations, policies, and prior incidents. Record where evidence is incomplete. For example, a contract may describe supplier access limits while current access logs show how those limits work in practice.
Scoring workshop. Agree what likelihood and impact mean for your business before ranking findings. Use consequences people can evaluate, such as lost access to production, exposure of customer records, or missed recovery objectives. Document the assumptions behind the rating so the customer can revisit it as evidence changes.
Delivery and follow-through. Review the ranked register with business and technical owners. Give each action a due date and a way to verify completion. Agree who can accept remaining risk and when they must review it. Where follow-up is in scope, revisit overdue actions and re-rate the risk once the fix is verified.
What to check: A useful risk register is a decision record. Each important entry needs an owner, a next action and a date to revisit it.
Practical details and examples
Choose a boundary leadership will recognise
An assessment can cover an organisation, a migration, a product or a particular process. A sensible boundary follows the business decision. If leadership needs to approve a new supplier, look at the data, permissions, dependencies and alternatives involved in that relationship. If the decision is a cloud migration, include identity, the workload, operational support and the effects of transition. State what you cannot assess because evidence or access is unavailable. A precise scope makes findings easier to apply and reduces confusion when people compare reviews.
CyberSeal’s methodology spans information security, cloud, applications, identity, third parties and compliance mapping according to scope. Start with the areas most likely to affect the decision, and agree who can explain each one. The solution architect or assessment lead can use interviews, document review and approved technical evidence to build a picture. Check findings with the people closest to the process before rating the risk. They may know about a protection that is not on a diagram or an exception that changes the practical impact.
Example: Decide what to do about standing vendor access
Suppose a vendor has a persistent administrator account for an application. The technical finding is broad access, but the business risk depends on what the application can reach and when the vendor needs to use it. If it contains customer data and a single account can reach production and backups, the impact may be significant. If access is monitored, approved per use and restricted to a small environment, the assessment may reach a different conclusion. Verify those conditions instead of scoring on the title of the finding alone.
Possible treatments include limiting the vendor role, introducing approved temporary access, or reducing what the account can reach. Consider the support agreement and the risk of disrupting urgent maintenance. Work with the customer to choose a practical option, record who owns the change and agree what proof will show the risk has reduced. If management decides to keep the existing approach for a limited period, document why, what interim protections apply and when that decision needs to be revisited.
Separate findings, assumptions and decisions in the risk register
Record the evidence in terms a reviewer can check. Then describe the scenario and what makes it plausible. Use a risk scale the customer understands, and explain the assumptions behind likelihood and impact rather than treating the score as a calculation of exact probability. A finding that matters to one company may be less urgent for another with different data, system exposure or operating constraints. Use a consistent method so similar decisions can be compared across teams.
Keep the risk treatment visible. Each entry should identify the business owner, recommended action, estimated effort or dependency and a review date. Where a change is not within the assessment scope, assign the work to the right internal or external team. Where implementation help is agreed, define who approves the plan and checks results. A good executive summary highlights the decisions that need attention now and explains the impact of waiting, instead of reproducing every technical observation.
Review progress with owners after delivery
At handover, review high-priority entries with the people responsible for carrying them out. Test whether they can explain what they need to do and how they will know when the treatment works. If an item depends on a vendor contract, funding or a future release, name that dependency so the business can plan around it. For ongoing risk tracking, agree a review cadence and what events should trigger a new assessment, such as a material architecture change or a new supplier with sensitive access.
In the next meeting, distinguish work completed from risk reduced. A new policy may establish responsibility but the exposure may remain until the control is implemented and tested. A temporary workaround may reduce likelihood without reducing the consequence if the event happens. Make those distinctions visible. This keeps the customer relationship focused on decisions and results rather than producing a new document every time the organisation meets.
What to bring to the first risk workshop
Bring a business objective, a current system or process diagram, and examples of past incidents or concerns with sensitive details removed. Ask the assessor to walk through one finding from evidence to decision, then show what the owner would receive. That short exercise is a useful way to check whether the assessment will help both leadership and the technical team.
Cybersecurity risk register template
Copy these columns into a spreadsheet or ticket. The sample below is illustrative. Use your own rating scale and review dates.
- Risk scenario and evidence
- A supplier’s standing admin account can access production backups. Evidence includes its role assignment and backup permissions.
- Likelihood, impact, and rationale
- Example rating: high priority. Standing access creates an ongoing opportunity for misuse, and backup deletion could delay recovery.
- Treatment, owner, and due date
- The identity lead replaces standing access with approved time-limited access. Agree a target date with the service owner.
- Verification and remaining risk
- Confirm the supplier can still complete approved tasks and is denied backup administration. Review any exception, its approver, and its expiry.
Frequently asked questions
How is this different from a vulnerability scan?
A scan finds technical exposures. An assessment connects technical and operational evidence to the consequences the business needs to manage.
Can we use it before a migration or audit?
Yes. Define which decisions and evidence are needed, and use the resulting priorities to plan changes before the deadline.